The GitHub Leak: How Artex's Exposed Secrets Highlight a Growing DevOps Nightmare
A breach at Artex involving exposed GitHub secrets underscores the catastrophic risks of improper credential management in modern software development.
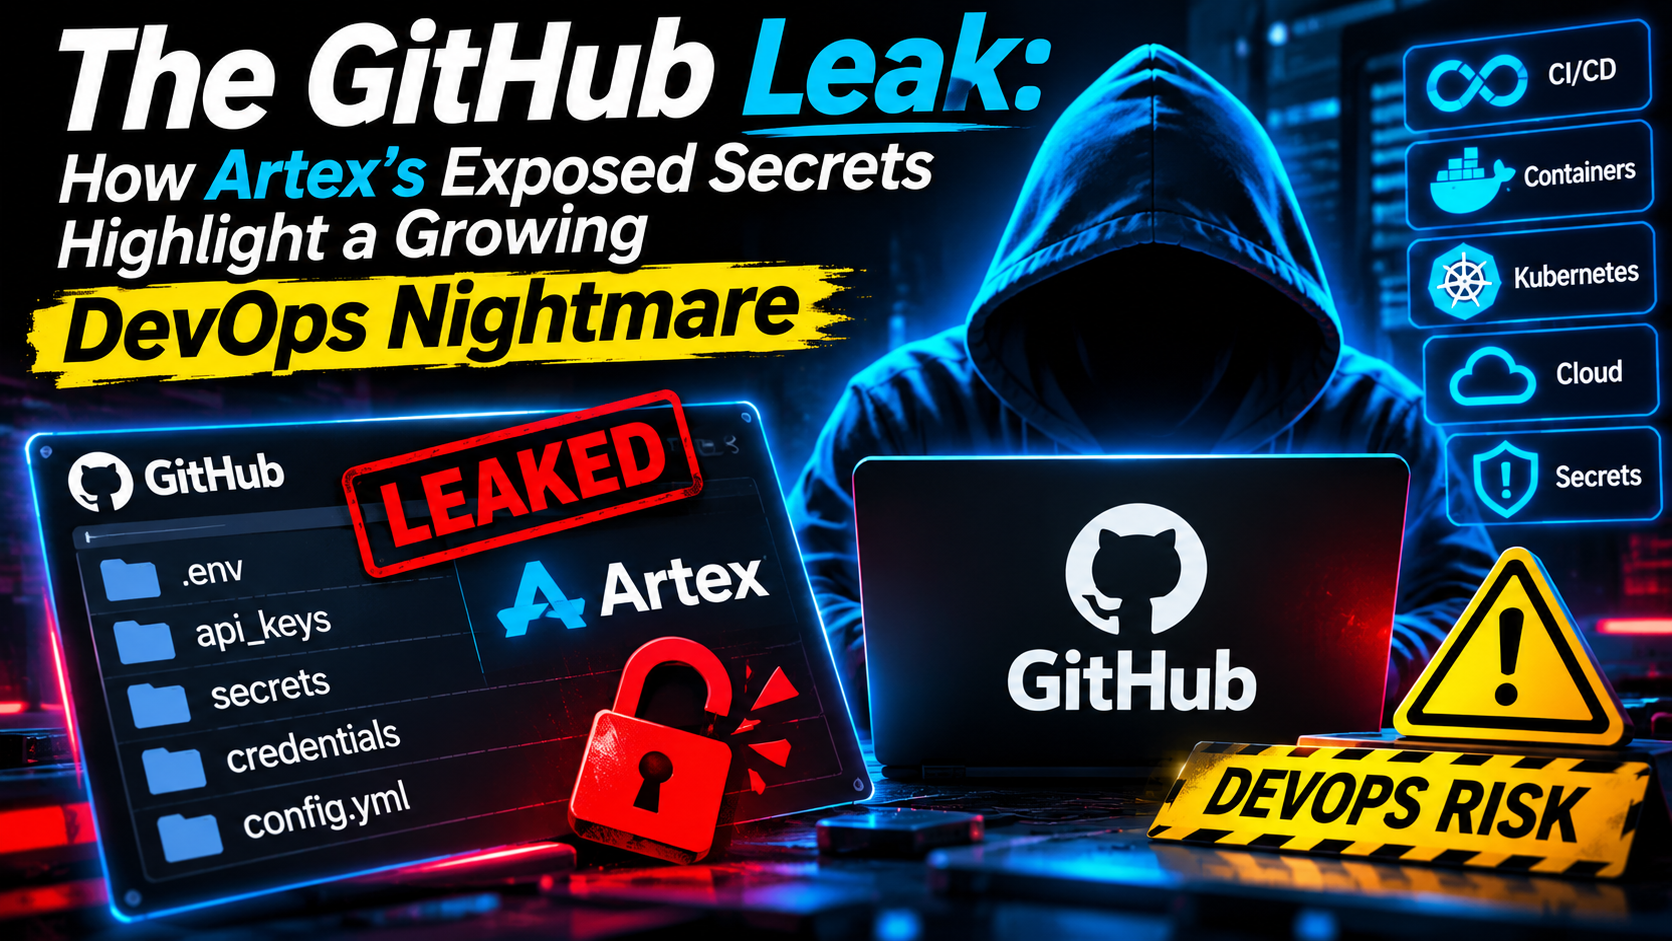
In the high-velocity world of modern software engineering, the line between a productive deployment and a catastrophic security breach is often a single, misplaced line of code. A recent security incident involving Artex has brought this reality into sharp focus, as hackers successfully exploited exposed secrets within the company's GitHub repositories.
This is not an isolated incident, but rather a symptom of a systemic vulnerability in the DevOps lifecycle. For developers, the convenience of version control often clashes with the rigorous demands of secret management, creating a playground for automated attackers looking for the next big entry point into corporate infrastructure.
The Anatomy of a Secret Leak
The Artex incident follows a pattern that has become all too common in the cybersecurity landscape. It begins with a developer, likely under pressure to meet a deployment deadline, accidentally hardcoding a sensitive credential—an API key, a database password, or a cloud service token—directly into a source file.
When that file is committed and pushed to a GitHub repository, the secret is no longer just a local configuration detail; it becomes part of the permanent digital record. Even if the developer realizes the mistake moments later and deletes the line of code in a subsequent commit, the secret remains etched in the Git history.
The Role of Automated Scrapers
One of the most misunderstood aspects of this threat is the speed of exploitation. Hackers do not sit around manually browsing through thousands of repositories. Instead, they employ highly sophisticated, automated bots that monitor the GitHub 'public feed' in real-time.
These bots are programmed to scan every single commit for patterns matching known credential formats (such as AWS access keys, Stripe tokens, or OpenAI API keys). The window between a secret being pushed to a public repository and it being detected by a malicious actor is often measured in seconds, not minutes. In the case of Artex, these exposed secrets provided the keys to the kingdom, allowing unauthorized actors to bypass traditional perimeter defenses.
Why 'Deleting' Isn't Enough: The Git Persistence Problem
For the technical community, the most critical lesson of the Artex breach is the fundamental nature of Git. Git is designed to be an immutable ledger of changes. When you perform a git rm or simply delete a line of code and commit the change, you are merely adding a new state to the repository. The old state, which contains the secret, is still preserved in the .git directory.
An attacker doesn't need your current main branch to be secure; they only need to run a git checkout on a previous commit or use tools to traverse the object database to find the sensitive string. To truly remove a secret, a developer must rewrite the entire repository's history—a process that is both destructive and complex.
Building a Defense-in-Depth Strategy
The Artex incident should serve as a catalyst for organizations to move away from reactive security and toward proactive, automated secret management. Relying on developer discipline is a failed strategy; security must be baked into the tooling.
1. Implementation of Pre-Commit Hooks
The first line of defense should be at the developer's workstation. By using pre-commit hooks, organizations can prevent secrets from ever leaving the local environment. Tools like Gitleaks or detect-secrets can be configured to run locally every time a developer attempts a git commit. If the tool detects a high-entropy string or a known pattern (like an AWS key), it aborts the commit process, forcing the developer to sanitize the code before it reaches the remote server.
2. Automated Scanning in CI/CD Pipelines
While pre-commit hooks protect the local environment, they can be bypassed. Therefore, a secondary layer of defense must exist within the Continuous Integration/Continuous Deployment (CI/CD) pipeline. Every pull request should trigger an automated scan of the entire commit history. If a secret is detected, the build should fail immediately, and the security team should be alerted.
3. Transitioning to Dedicated Secret Management
Hardcoding secrets—even in private repositories—is a dangerous practice. The industry standard is to decouple configuration from code using dedicated secret management services.
- HashiCorp Vault: Provides a centralized way to manage secrets, offering dynamic secrets that expire after a set period.
- AWS Secrets Manager / Azure Key Vault: Cloud-native solutions that integrate seamlessly with identity and access management (IAM) roles, ensuring that applications only receive the credentials they need at runtime.
- Environment Variables: While better than hardcoding, environment variables should still be injected via a secure orchestrator (like Kubernetes Secrets) rather than being stored in
.envfiles that might accidentally be committed.
The Recovery Protocol: What to do when a leak occurs
If a secret is exposed, the response must be immediate and clinical. Following a 'delete and commit' approach is a recipe for continued compromise. The following steps are mandatory:
- Revoke and Rotate: Immediately invalidate the compromised credential at the source (e.g., rotate the AWS key or the Stripe token). Assume the key is already in the hands of an attacker.
- Audit Logs: Check the logs for the service associated with the leaked key to identify any unauthorized activity or data exfiltration.
- Rewrite History: If the repository must remain, use tools like
git filter-repoor the BFG Repo-Cleaner to scrub the secret from the entire Git history. This is a destructive operation and requires coordination with the entire development team. - Analyze the Root Cause: Determine how the secret bypassed existing checks to prevent a recurrence.
Conclusion
The Artex breach is a stark reminder that in the modern era, code is not just logic; it is also a carrier for highly sensitive access credentials. As development cycles accelerate and the number of interconnected APIs grows, the surface area for these leaks expands exponentially. For the technical professional, the lesson is clear: security is not a feature to be added at the end of a sprint—it is a fundamental requirement of the development environment itself.